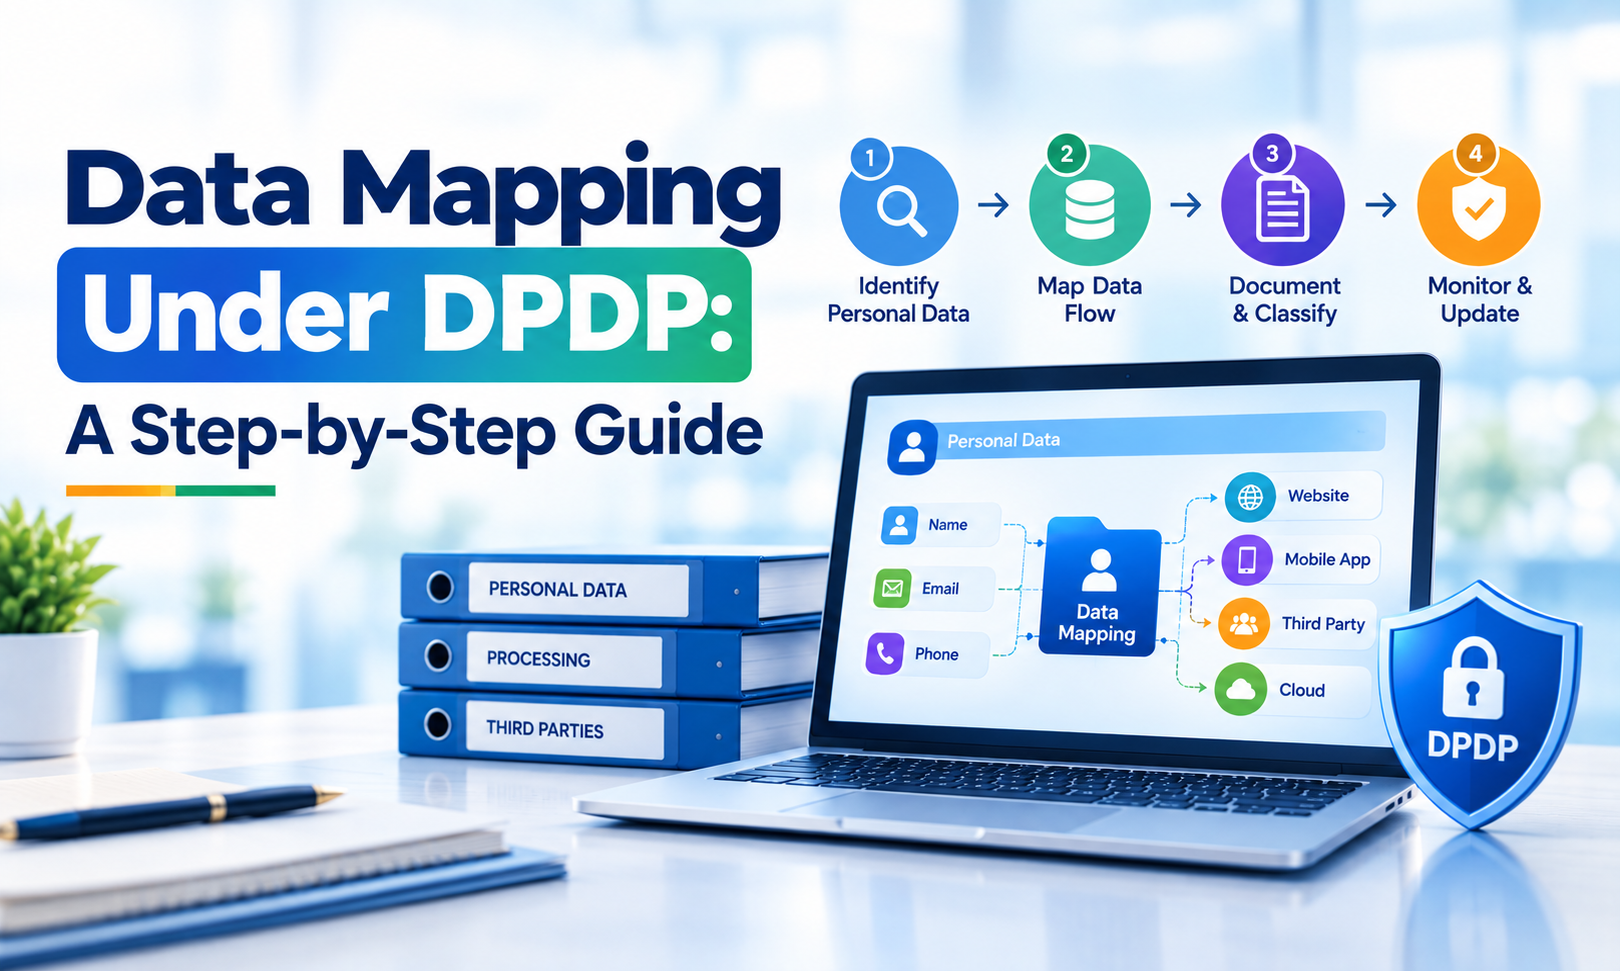
Data Mapping Under DPDP: A Step-by-Step Guide
A step-by-step guide to mapping personal data flows under DPDP — from entry points and internal system hops to external transfers and retention triggers — distinct from a static data inventory.
Stay ahead of India's evolving data protection landscape with expert analysis, practical guidance, and the latest updates on the DPDP Act — simplified for professionals like you.
A step-by-step guide to mapping personal data flows under DPDP — from entry points and internal system hops to external transfers and retention triggers — distinct from a static data inventory.
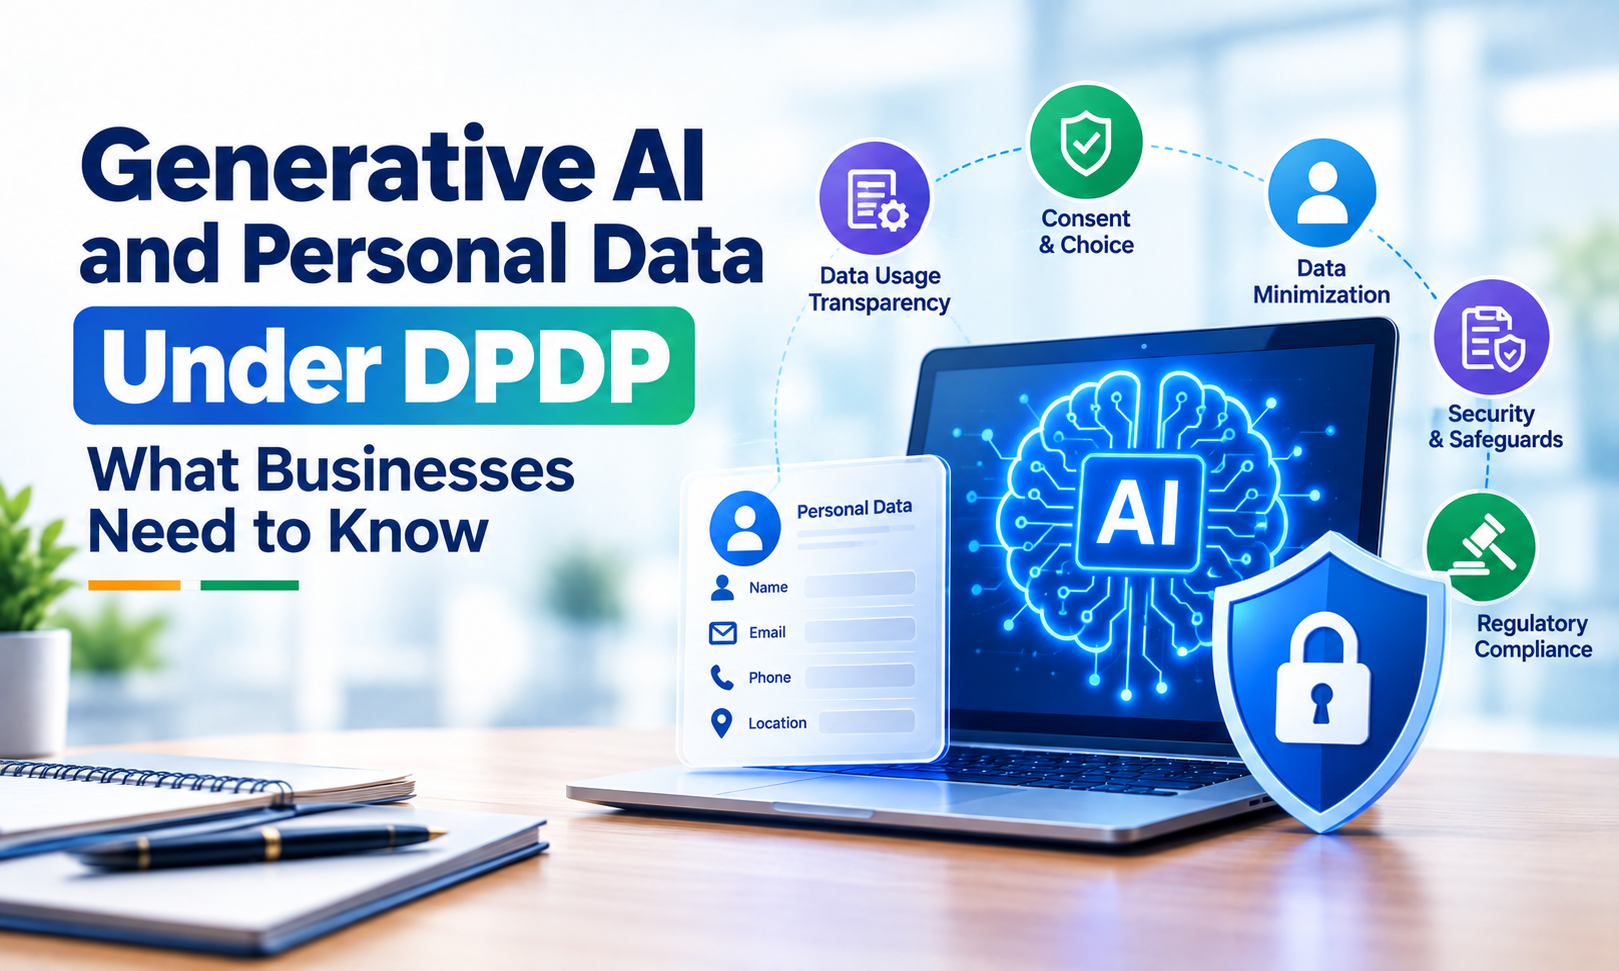
Covers the specific DPDP risks generative AI creates — employee prompt leakage, customer-facing chatbots becoming data controllers, and hallucinated personal data as an accuracy problem — plus a practical usage policy.
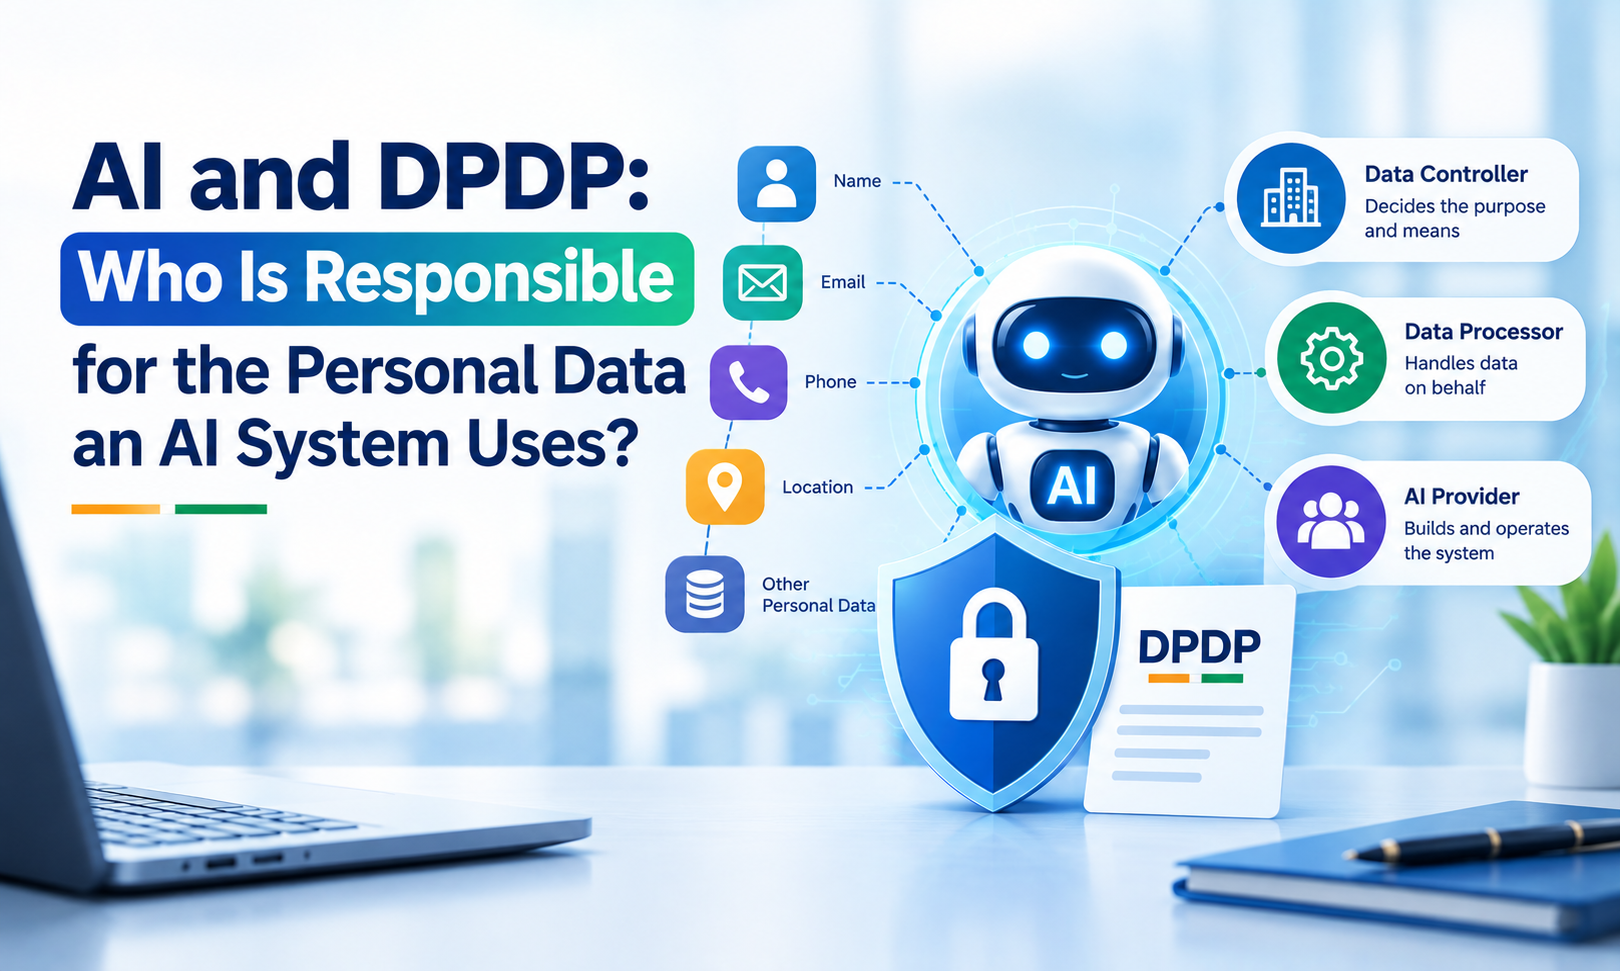
Unpacks who's accountable under DPDP when an AI system processes personal data — vendor contract red flags, the training-data consent gap, and why Section 9's children's-data rules apply regardless of the technology.
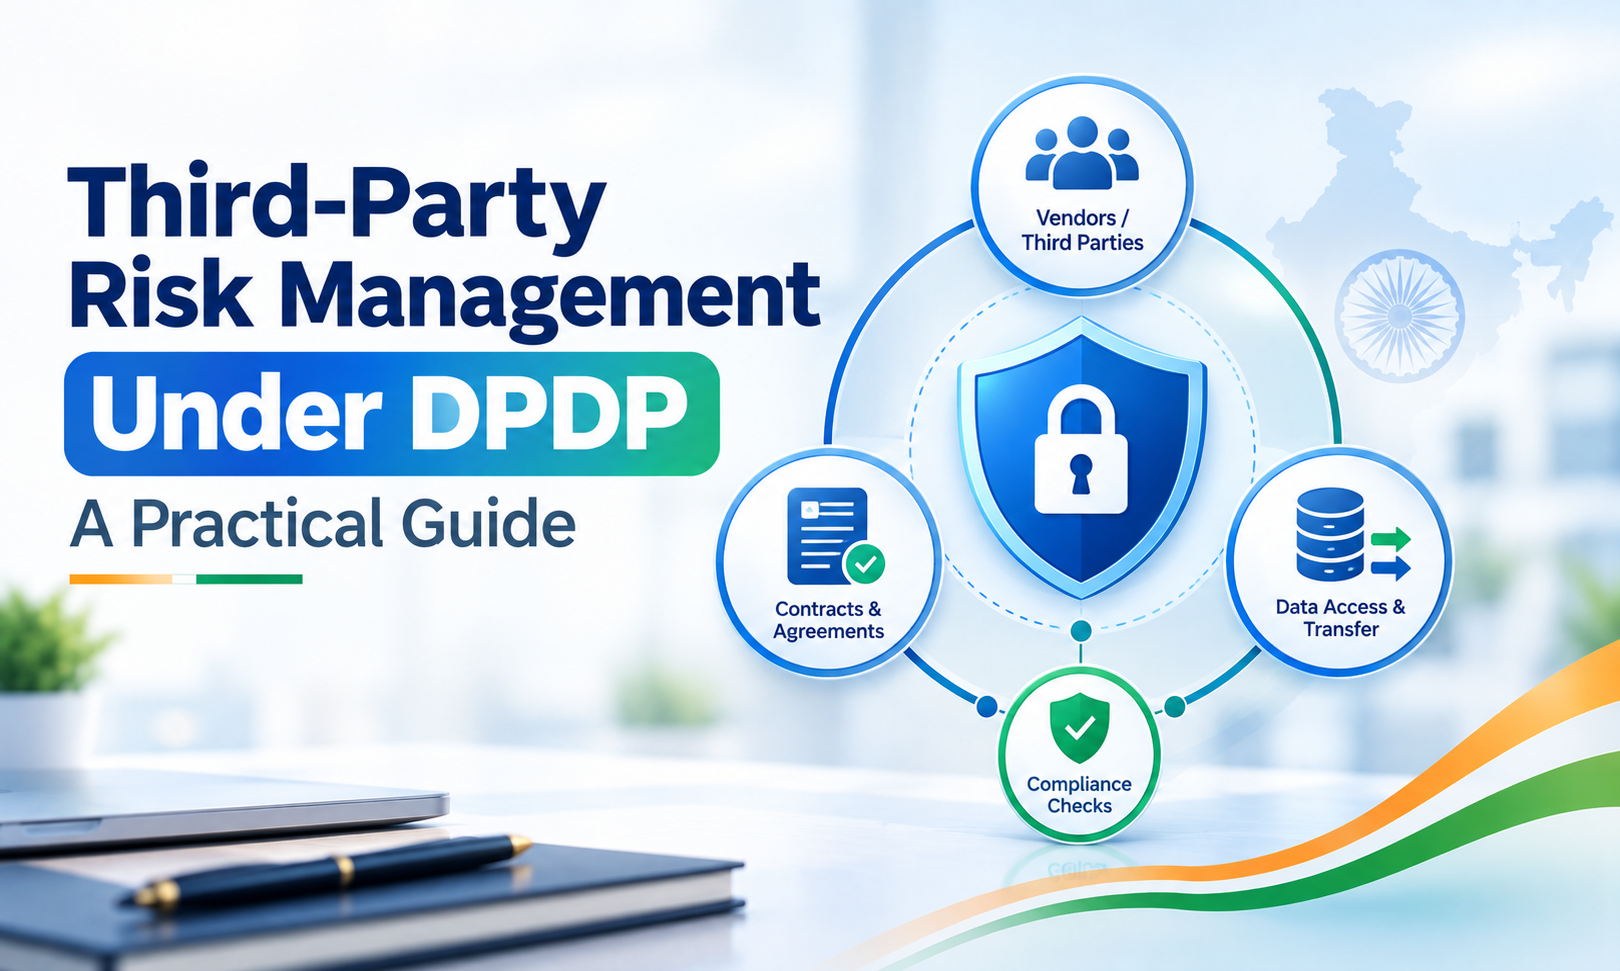
A practical five-step framework for managing vendor risk under DPDP — classifying Fiduciaries vs. Processors, building enforceable contracts, and closing the gaps that create real compliance exposure.
Explains what actually triggers a DPDP Board inquiry, what evidence the Board can demand under Sections 28 and 36, and where the gap between policy and proof most often catches businesses out.
Defines what qualifies as a personal data breach under Section 2(u) of the DPDP Act, the 72-hour notification requirement, and why "we didn't think it was serious" isn't a valid reason to skip reporting.
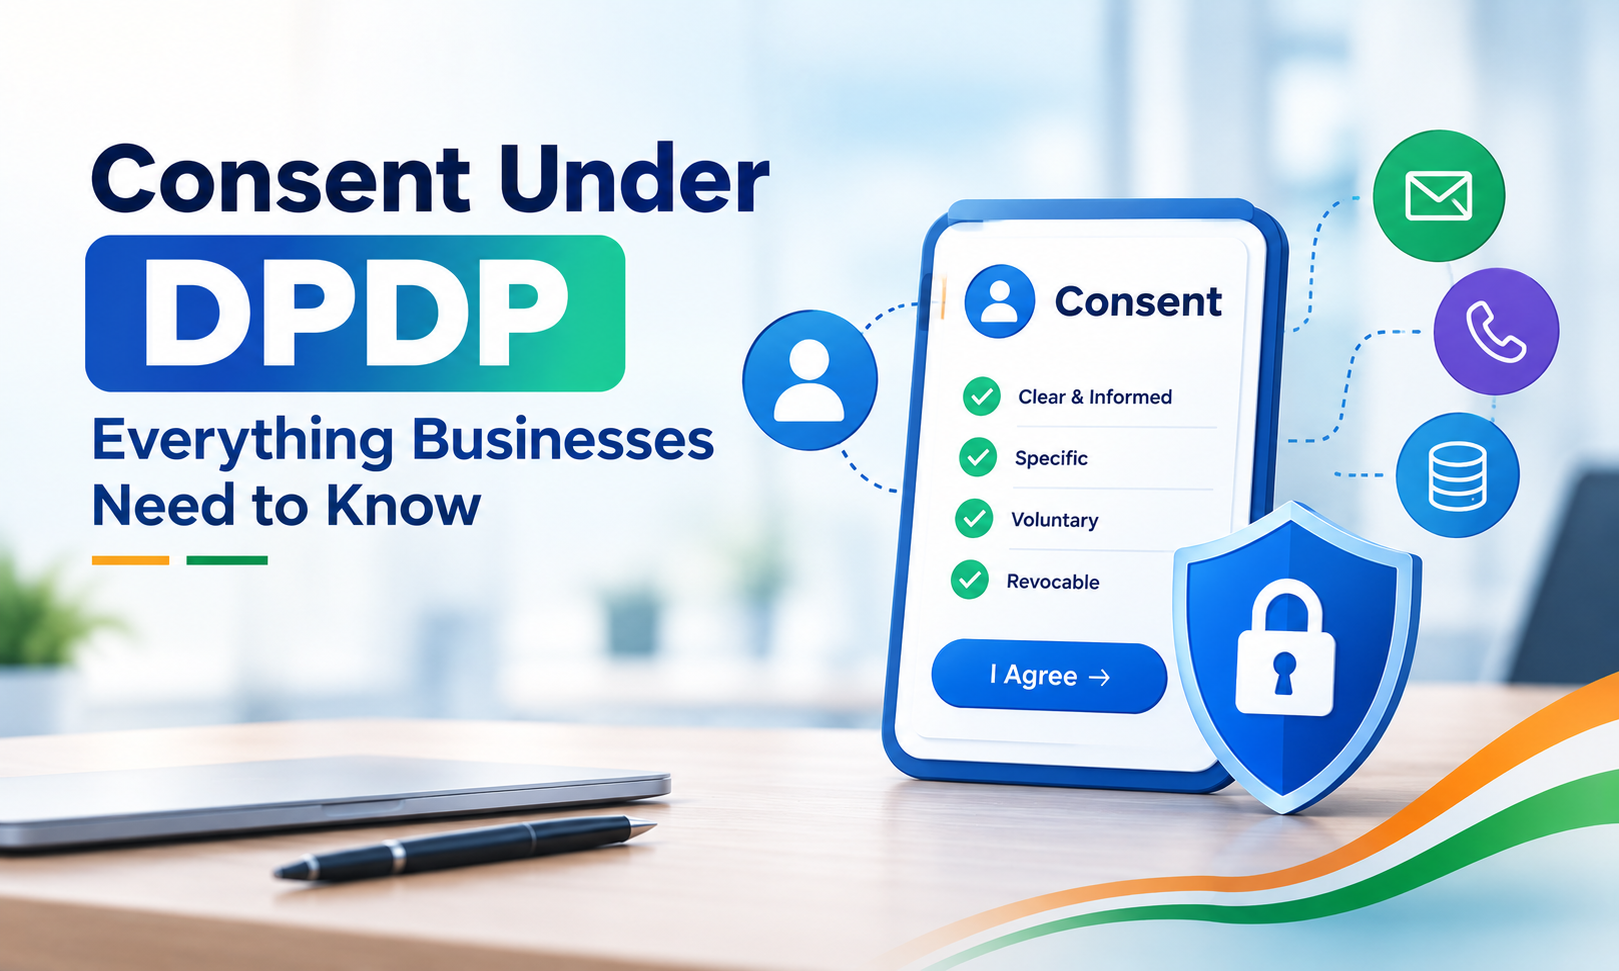
A deep dive into what valid consent under the DPDP Act actually requires — notice, the five validity conditions, legitimate-use exceptions, withdrawal mechanics, and where most businesses get it wrong.
A practical guide to building a DPDP-compliant data inventory — what fields to capture, how to run discovery, and the categories of data businesses most often miss.
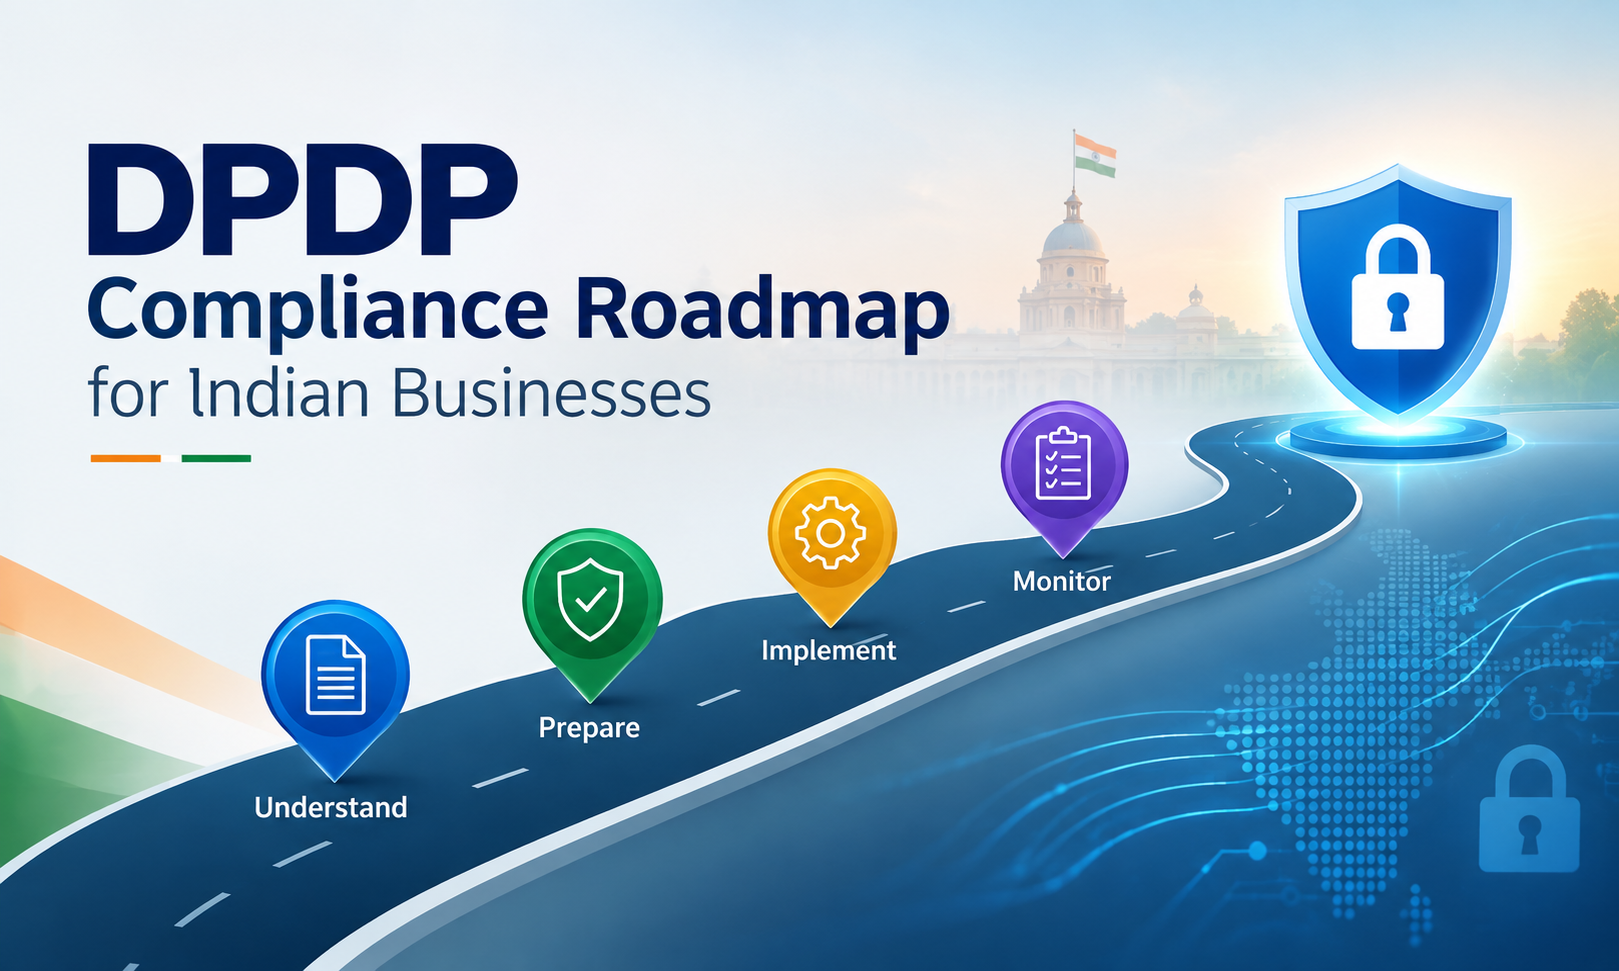
Lays out a staged DPDP compliance roadmap — from data discovery through vendor contracts and breach readiness — mapped against the regulatory timeline running up to May 2027.
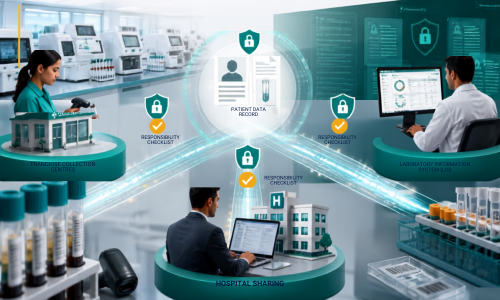
Untangles Fiduciary vs. Processor roles across a diagnostic lab's franchise counters, LIS vendors, and hospital referrals — and what a valid Section 8(2) processor contract must actually contain.
Explains why hospital DPDP compliance breaks down when consent lives only in the HIS — and how patient data flowing through labs, imaging, pharmacy, and TPAs needs one coherent notice-and-consent story instead.
Breaks down how school admission forms — Aadhaar copies, photos, medical and income fields — quietly violate DPDP Act purpose-limitation and children's-consent rules, and how to fix them before May 2027.
Covers the DPDP Act's origins, core structure (Data Principals, Fiduciaries, consent, rights, penalties), the phased 2025–2027 rollout timeline, and why compliance is an operational program, not just a legal checkbox.
Breaks the DPDP Act into plain-English terms — decoding key roles, what valid consent actually requires, and data rights individuals can exercise — for non-legal, business-decision-maker readers.
Breaks down what the DPDP Rules 2025 actually require — notices, consent, breach reporting, children's data — plus the 3-phase rollout timeline and penalty structure businesses must plan around.


